NetScaler Zero-Days (CVE-2026-88771, CVE-2026-88772): Why AI Data Planes Need Continuous Patching
Citrix disclosed eight NetScaler CVEs with two exploited zero-days and no workaround. Administrators had two options: patch, or power it off. Here is a per-CVE analysis of what an Envoy-based Agent Router in front would have changed (four structurally mitigated, two reduced, two better handled at another layer) and the lesson that matters most for the AI data planes now going into production: the edge you can patch continuously is the edge you can defend.
 Tetrate Engineering Team
On September 27, 2026, Citrix published security bulletin CTX697096 covering eight vulnerabilities in NetScaler ADC and NetScaler Gateway. Two are remote code execution flaws scoring CVSS 9.5 that were already being exploited as zero-days, and the bulletin offers no workaround for either one. If you run NetScaler, upgrade to 14.1-73.37 or 13.1-64.23 now, and check for compromise before you do. This post is about the architectural question underneath, and why it applies with even more force to AI data planes: when an internet-facing data plane has a pre-authentication RCE and the vendor has no mitigation, how many options does your architecture give you, and how fast can you patch?
Key facts
- What: Eight vulnerabilities in NetScaler ADC and NetScaler Gateway, disclosed together in CTX697096 on September 27, 2026.
- Exploited: CVE-2026-88771 and CVE-2026-88772, both CVSS 4.0 9.5, both added to the CISA Known Exploited Vulnerabilities catalog. Exploitation was discovered during forensic investigations.
- Reach: CVE-2026-88771 affects every deployment in its default configuration — no feature needs to be enabled. CVE-2026-88772 requires DTLS, which is on by default for VPN virtual servers.
- Workaround: None published for either exploited flaw. The only configuration-level fix in the bulletin addresses CVE-2026-88778, the least severe issue on the list.
- Fixed builds: 14.1-73.37 and later, 13.1-64.23 and later, 14.1-73.37 FIPS, and 13.1-37.279 for FIPS/NDcPP.
- Before patching: CISA advises checking for indicators of compromise first, because applying updates may destroy forensic evidence.
- Credit: Michael Tucker, Chew Keong Tan, and Alex Bernier of the JPMorgan Chase XOR Team, and Maxim Suhanov.

Agent Router is Tetrate's Envoy-based AI data plane — AI Gateway, MCP Gateway, and AI Guardrails — built on Envoy AI Gateway by its creators, and kept continuously patched by the Tetrate Patch Service.
A weekend with two options
The public record started before the bulletin did.
On Saturday September 26, administrators across Europe began receiving calls from security teams and national CERTs advising them to shut their NetScalers down immediately. No CVE. No advisory. No indicators of compromise. A thread on r/Citrix collected the pattern in real time: one organization after another reporting the same phone call and the same absence of detail, with the underlying information apparently held under restricted distribution. One customer relayed a line from Citrix confirming teams were working around the clock on a fix. Another guessed — correctly, as the bulletin later confirmed — at pre-authentication memory corruption on the Gateway path.
Organizations took production VPN offline for roughly thirty-six hours on the strength of a phone call, because the alternative was leaving an unpatched pre-auth RCE facing the internet.
That is the part worth examining. Not the vendor — F5, Fortinet, Cisco, and Palo Alto have all had their turn and will again — but the fact that the architecture offered exactly two responses: patch when a patch exists, or power it off. Both are expensive. One was unavailable.
It is also worth examining because the same shape is forming around a new class of infrastructure. AI data planes — the gateways that broker every model call, every MCP tool invocation, and every agent’s credentials — are becoming internet-facing edge components in their own right. If patching them is an event rather than a continuous process, they will eventually produce a weekend like this one.
The eight vulnerabilities
Preconditions matter more than scores here, because they determine what is actually reachable.
| CVE | CVSS 4.0 | Class | Precondition |
|---|---|---|---|
| CVE-2026-88771 | 9.5 | RCE — improper input validation (CWE-20) | Every deployment. Default configuration. |
| CVE-2026-88772 | 9.5 | Memory overflow → RCE/DoS (CWE-119) | DTLS enabled — on by default for VPN vservers |
| CVE-2026-88773 | 9.3 | HTTP request smuggling (CWE-444) | Any lb, cs, vpn, or authentication vserver of type HTTP or SSL |
| CVE-2026-88774 | 7.0 | Feature policy bypass (CWE-16) | Any policy expression using an HTTP URL-based expression |
| CVE-2026-88775 | 8.8 | Memory overflow → DoS (CWE-119) | Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver |
| CVE-2026-88776 | 8.8 | Memory overflow → DoS (CWE-119) | LB vserver of type Oracle |
| CVE-2026-88777 | 8.8 | Memory overflow → DoS (CWE-119) | Non-HTTP L7: FTP ALG (on by default on LSN groups), RTSP ALG, DNS64, NAT64 |
| CVE-2026-88778 | 8.8 | TCP ISN prediction (CWE-342) | Any TCP-family vserver and Enhanced ISN Generation disabled |
Structural mitigation beats signature mitigation
The instinct when a CVE lands is to write a detection rule for it. That instinct is right, and it is also structurally too slow, because a rule requires knowing the vulnerability.
On Friday, nobody knew. On Saturday, people knew something existed but not what. The rule became writable on Sunday afternoon — after two days of exposure, and after the appliances had already been powered off. No amount of operational discipline closes that gap, because the gap is set by disclosure, not by process.
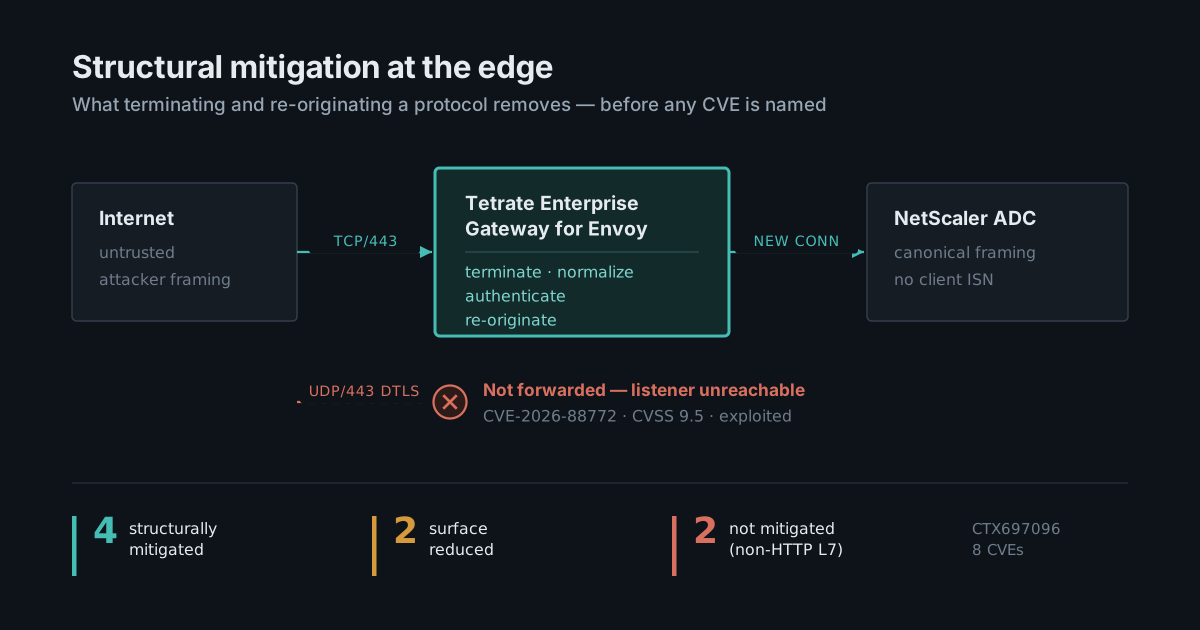
There is a second category of mitigation that has no such dependency. A proxy that terminates a protocol and re-originates it eliminates entire vulnerability classes by construction, before anyone has named them:
- When a gateway terminates a TCP connection and opens a new one upstream, the appliance never sees the client’s initial sequence numbers.
- When it parses an HTTP request and re-serializes it, the appliance never sees the attacker’s framing — only canonical framing the gateway generated.
- When it fronts port 443 over TCP, it does not forward UDP, so a DTLS listener behind it is not reachable at all.
None of this required knowing that CVE-2026-88772 exists. These properties were already true on Friday. That is the distinction worth designing around: signature mitigation is reactive with a latency floor set by disclosure, while structural mitigation is already in place, with the trade-off that it only covers what the protocol boundary actually touches.
Which is why the scorecard below has three verdicts and not one.
What a gateway in front actually changes
We graded all eight against an Agent Router deployment sitting in front of the appliance. Agent Router is built on Envoy Gateway, so the same Envoy protocol handling and Gateway API policies apply to it. Four are structurally mitigated, two have their attack surface meaningfully reduced, and two are better addressed at a different layer. We list those two with the same prominence as the successes, because knowing where a gateway is the wrong tool is as useful as knowing where it is the right one.
Structurally mitigated
CVE-2026-88772 — DTLS memory overflow (exploited). DTLS is datagram TLS, carried over UDP. A gateway terminating HTTPS on TCP/443 does not forward UDP/443. If the appliance is not independently routable from the internet, the vulnerable parser is never fed attacker-controlled bytes. Citrix’s own precondition table confirms that -dtls OFF removes exposure; fronting achieves the same reachability outcome at the network layer without touching the appliance configuration. Note the trade-off: DTLS carries EDT transport for HDX, so removing it moves those sessions to TCP, with the performance implications that entails.
CVE-2026-88773 — HTTP request smuggling. Smuggling requires two parsers disagreeing about where one message ends and the next begins. Envoy rejects any HTTP/1.1 message carrying both Content-Length and Transfer-Encoding; its HTTP/1 codec cites RFC 7230 §3.3.3 and names request smuggling as the reason, and it has held that deliberately strict position against years of requests to relax it. More important than the rejection is the re-serialization: the appliance receives framing that Envoy generated, never the bytes the attacker sent. Running HTTP/2 upstream removes the ambiguity entirely at the framing layer.
CVE-2026-88774 — feature policy bypass. This is path confusion: a URL form that the appliance’s policy expression does not match but that the request nonetheless resolves to. Agent Router inherits Envoy Gateway’s defaults, which already address this class. Slash merging is on by default, and escapedSlashesAction defaults to UnescapeAndRedirect, whose API documentation states that it “minimizes possibility of path confusion exploits by forcing request with unescaped slashes to traverse all parties.” Organizations wanting a fail-closed posture can set RejectRequest instead. The more durable fix is to stop depending on appliance policy expressions for authorization at all — which we return to below.
CVE-2026-88778 — TCP ISN prediction. Off-path TCP injection requires predicting the initial sequence number of the connection being targeted. With a gateway in front, the internet-facing connection terminates on Envoy, and its ISN comes from the Linux kernel’s RFC 6528 generator. The appliance’s weaker ISN is only ever exposed on an internal leg that an external attacker is off-path to. To be clear about precedence: Citrix ships a real one-line fix here — enable Enhanced ISN Generation — and that is the primary remedy. The gateway is defense in depth.
Surface reduced, not eliminated
CVE-2026-88771 — the flagship RCE (exploited). No technical vector has been published, so a gateway in front may not be the right place to claim a block on this one. Two cases apply. If the vector is on the management plane, the data-plane gateway is not the best place to address it; network isolation of the management interface is, and that interface should not face the internet under any architecture. If it is on the data plane, every request is parsed, normalized, and re-serialized before reaching the appliance, which defeats input that depends on parser quirks. What a gateway provides unconditionally is a positive security model: a Citrix Gateway’s legitimate URL surface is small and enumerable, and most input-validation RCEs live on endpoints that no legitimate client ever calls. Narrowing what is reachable is a real reduction against an unknown vector. It is not a block, and we will not describe it as one.
CVE-2026-88775 — Gateway and AAA denial of service. Connection limits, rate limiting, a request header cap returning 431, and a request-received timeout returning 408 bound the malformed and high-volume cases at the edge. If the trigger turns out to be a single well-formed request to a legitimate endpoint, edge rate controls may not be the best tool for it. The larger move is architectural: authenticate at the gateway, and the AAA virtual server no longer needs to face the internet at all. That deletes the precondition rather than filtering traffic against it.
Better addressed elsewhere
CVE-2026-88776 — Oracle LB virtual server. Agent Router is designed for HTTP, gRPC, and AI and MCP traffic; the Oracle TNS protocol sits outside that scope, so a gateway may not be the best place to address this one. Network segmentation is the better control — a database load balancer should not be internet-facing — and that is a firewall property rather than a gateway one.
CVE-2026-88777 — FTP and RTSP ALG, DNS64, NAT64. Application-layer gateways for FTP and RTSP, DNS64, NAT64, and carrier-grade NAT are not functions an HTTP or AI gateway is designed to perform, so it may not be the best place to handle them. This one is strategic rather than tactical: these are the accumulated features of a general-purpose appliance, and moving north-south HTTP traffic off it is what eventually makes retiring them possible.
Making the reactive path fast, too
Structural mitigation covers what the protocol boundary touches. Everything else still needs a rule — and the question becomes how quickly a rule can be written, shipped, and verified.
This is where Built On Envoy (BOE) matters. BOE compiles Go extensions into Envoy dynamic modules, and the catalog already includes the components this scenario calls for: a WAF built on OWASP Coraza with the Core Rule Set embedded, an OpenAPI request validator for positive-security allowlisting, and inline Cedar and OPA authorization for moving policy decisions to the edge. Envoy Gateway’s own dynamic modules documentation uses the BOE Coraza module as its worked example, and because Agent Router runs on Envoy Gateway, the same modules attach to it the same way.
Two capabilities matter during an incident like this one.
You are not waiting on a vendor. When a vector or an indicator of compromise is published, the mitigation is a rule you write or a filter you compile, deployed at the edge on your own timeline.
Telemetry lives off the appliance. Citrix makes indicators of compromise available through NetScaler Console, which depends on telemetry from the appliance itself — the same device that may be compromised. Several administrators in that Reddit thread reported finding nothing in their logs and asked what they should even be looking for. A gateway in the request path produces an independent record of every request that reached the appliance, which is what makes retrospective hunting possible once indicators finally land. That record requires no knowledge of the CVE, which means it would already have been running on Friday.
Configuring it
The hardening below is declarative policy on the Gateway resource Agent Router runs on, versioned like any other configuration. Complete, runnable manifests are available in the Built On Envoy repository.
Start with the protocol-level hardening that produces the structural mitigations:
apiVersion: gateway.envoyproxy.io/v1alpha1
kind: ClientTrafficPolicy
metadata:
  name: netscaler-edge-hardening
spec:
  targetRefs:
    - group: gateway.networking.k8s.io
      kind: Gateway
      name: eg
  path:
    # Fail closed on %2F/%5C rather than normalizing and forwarding.
    # Addresses the path-confusion class behind CVE-2026-88774.
    escapedSlashesAction: RejectRequest
    disableMergeSlashes: false
  headers:
    # Bound oversized header attacks at the edge; returns 431.
    maxRequestHeaderLimit: 32Ki
  timeout:
    http:
      # Cap slow-request starvation; returns 408.
      requestReceivedTimeout: 10s
      idleTimeout: 60s
  connection:
    bufferLimit: 64Ki
Then attach the WAF as a dynamic module. The EnvoyProxy resource must declare the module in its allowlist before an EnvoyExtensionPolicy can reference it:
apiVersion: gateway.envoyproxy.io/v1alpha1
kind: EnvoyExtensionPolicy
metadata:
  name: netscaler-waf
spec:
  targetRefs:
    - group: gateway.networking.k8s.io
      kind: Gateway
      name: eg
  dynamicModule:
    - name: composer
      filterName: coraza-waf
      config:
        mode: FULL
        directives:
          - "Include @coraza.conf"
          - "SecRuleEngine On"
          - "Include @crs-setup.conf"
          - "Include @owasp_crs/*.conf"
For the positive security model that narrows the reachable surface against an unknown vector, the OpenAPI validator restricts traffic to the Gateway’s legitimate URL surface. Deploy it in dry_run mode first and review what it would have rejected before enforcing — the endpoint inventory of a production Citrix Gateway is rarely exactly what anyone expects.
Continuously patching Agent Router and AI data planes
Placing a gateway in front of an appliance raises an obvious and fair objection: you have added another internet-facing component, so what keeps it patched?
That question matters even more for AI data planes. An AI gateway holds the provider credentials for every model behind it and the tokens for every MCP tool its agents can call. It sits in the path of prompts, tool arguments, and responses that routinely carry sensitive data. It is often reachable from the internet so that agents, SaaS tools, and developers can use it. And it is built on fast-moving code — Envoy, its AI extensions, MCP handling — that will receive CVEs like any other parser. A compromised AI data plane is not one exposed service; it is a key ring to every model and tool connected to it.
The NetScaler weekend is what happens when patching is an event: wait for disclosure, wait for a build, schedule a window, hope nothing broke. For Agent Router and every AI data plane you run, patching should be a loop that is always running.
The Tetrate Patch Service provides that loop. It delivers patches to Envoy data planes — including Agent Router — through a fully automated pipeline: it continuously scans the images actually running in your clusters, delivers patched builds, and reports back on whether each one landed.
Compared with the appliance case, where the compromise check depends on telemetry from the device under suspicion, and where the vendor’s own guidance is to preserve forensic evidence before patching because patching may destroy it:
| Appliance | Agent Router + Patch Service | |
|---|---|---|
| Patch cadence | Event-driven, after disclosure | Continuous |
| Patch unit | Firmware on an HA pair | A container image version |
| Patch action | Maintenance window and downtime | Automated patch delivery pipeline |
| Knowing you are exposed | Read the advisory, check ns.conf against eight precondition patterns | Continuous scan of images actually running |
| Proof it landed | Assumed | Agent-observed; continuous reporting on status of the infra |
| Custom mitigation | Wait for the vendor | Write a filter, ship it as a release |
| Forensics afterward | Patching may destroy evidence | Independent telemetry, off the affected device |
Things to keep in mind
- Fronting is not patching. Upgrade to 14.1-73.37 or 13.1-64.23. Everything here buys the ability to schedule that work deliberately rather than at 2am on a Saturday.
- A proxy in front may not be the best tool for a device that is already compromised. These were exploited as zero-days before disclosure, and a gateway will not remove a web shell that is already present. Hunt first, preserve evidence, then patch — in that order.
- Not every protocol moves. ICA and HDX, EDT over UDP, RDP Proxy, and CVPN are Citrix-proprietary, and a gateway may not be the best place to terminate them. This is a strategy for the HTTP north-south surface, not a replacement for the appliance.
- The Patch Service is scoped to your data planes, not your NetScaler. It reports on container images running in your clusters; an appliance is outside its scope. Its job is to keep Agent Router and your other Envoy data planes current, and provably so. Mitigating the appliance is the gateway’s job.
Designing for the next one
There will be another bulletin. It will name a different vendor, arrive on a different weekend, and carry different preconditions — and increasingly, it will name a component of the AI stack. What will not change is the shape of the problem: a pre-authentication flaw in something that has to face the internet, a vendor working on a fix, and an architecture that offers some number of options while you wait.
If that number is two, it is worth knowing before the next call comes in. A data plane you control, extensible in code, and continuously patched by a loop that proves its own work makes the number three. Four of these eight CVEs never reach the appliance at all — and that was already true before anyone had named them. For Agent Router and every AI data plane you put into production, the patch loop should already be running before the bulletin arrives, not after.
Vulnerability details in this post are reproduced from the vendor bulletin. No exploit detail is published here, and nothing in this analysis substitutes for applying the vendor’s fixed builds. If you suspect compromise, review Citrix’s guidance for suspected NetScaler compromise and preserve forensic evidence before patching.
To discuss placing Agent Router in front of legacy edge infrastructure, or continuously patching the AI data planes you already run, get in touch.
Tetrate Engineering Team