AI Ingress vs. AI Egress: Two Directions of AI Traffic, One Control Point
TL;DR: Tetrate Agent Router Enterprise governs AI traffic in both directions, so your team sets identity, token, and tool policy in one place and avoids a surprise model bill or an open path to outside tools.
AI ingress is traffic coming into your agents and self-hosted models. AI egress is traffic leaving your cluster for model providers and MCP servers. One Envoy data plane can govern both directions.
Teams often govern one direction and leave the other direction open. A team may add authentication at ingress and then let every agent call any model provider with a key copied into application code. Your finance team learns the cost from the invoice, and nothing warns you when an agent reaches a tool your team never approved.
Tetrate Agent Router Enterprise gives platform teams one control point for both directions. Agent Router Enterprise attributes traffic to a team, agent, and project at the gateway. Agent Router for Ingress covers requests coming into agents and self-hosted models in your cluster.
AI Ingress Is Traffic Coming Into Your Agents and Self-Hosted Models
Callers send prompts, files, and tool results to your agents. Callers also send inference requests to models your team runs on your own GPUs. The AI ingress gateway receives each request before the request reaches the agent or the model.
The ingress gateway checks caller identity. The ingress gateway checks token budgets and rate limits. The ingress gateway can reject a request with a prompt that breaks policy before your GPUs spend time on the request. What is an AI ingress gateway? covers the ingress controls in detail.
Ingress traffic carries a direct cost even when the model sits inside your cluster. Each request consumes GPU time. A caller with no limit can fill the queue and slow every other caller, and nothing warns you until users report slow answers.
AI Egress Is Traffic Leaving Your Cluster for Models and MCP Servers
Your agents call model providers such as OpenAI, Anthropic, and cloud model services. Your agents also call MCP servers that read files, query databases, and run tools outside the cluster. The AI egress gateway receives each call before the call leaves your cluster.
The egress gateway decides which destinations your agents can reach. The egress gateway adds provider keys on the way out, so application code carries a gateway key and no provider key. The egress gateway counts tokens per team, agent, and project. What is an AI egress gateway? covers the egress controls in detail.
Egress traffic creates the provider invoice. Egress traffic also carries prompt data outside your network. A gateway at the exit point can redact sensitive data, block a destination, and record the call for audit.
Agents Create More Egress Than Ingress
One user request can start a chain of agent work. The agent may call a model, call five tools, call the model again with tool results, and repeat the loop until the agent has an answer. The user sent one ingress request. The agent created many egress calls.
Human web traffic has a different pattern. A browser sends a request and receives a page. Agent traffic multiplies inside the cluster and then leaves the cluster. Platform teams that watch ingress dashboards miss most agent traffic because most agent calls point outward.
Cost and risk grow with egress volume. Each egress call can spend tokens, send data to a provider, or run a tool. Kubernetes egress for AI agents compares NetworkPolicy, service mesh egress gateways, and AI gateways for outbound agent traffic.
Each Direction Needs Different Controls
| Direction | Main risk | Controls at the gateway |
|---|---|---|
| AI ingress | An unknown caller spends your GPU time and token budget | Caller authentication, token limits per caller, rate limits, prompt checks |
| AI egress | An agent sends data to an unapproved model or tool and spends your provider budget | Destination allow list, provider key injection, token counts per team and agent, MCP tool policy |
| AI ingress | A caller floods a self-hosted model and slows other callers | Queue-aware routing, per-caller quotas, model access rules |
| AI egress | A looping agent repeats model calls for hours | Token limits per agent, budgets, rate limits, alerts |
The AI gateway glossary defines the core terms. AI gateway vs. API gateway explains how AI gateways differ from API gateways built for web traffic.
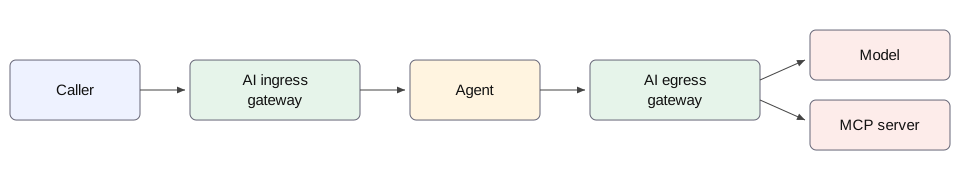
A caller reaches an agent through an AI ingress gateway. The agent reaches models and MCP servers through an AI egress gateway.
Two limits. A gateway governs traffic that passes through the gateway. An agent with a direct network path around the gateway keeps the direct path until you close the path with network policy. A gateway also records the identity on the request. A shared gateway key gives you shared attribution, so give each team and each agent a separate key.
One Control Point for Both Directions Stops Policy Drift
Separate tools for ingress and egress create separate policy lists. The ingress tool may allow a caller that the egress tool cannot name. The egress tool may count tokens for a team that the ingress tool calls by a different name. Reports stop matching, and audits take manual work.
One control point uses one identity model. A request enters with a caller identity. Agent work leaves with a team, agent, and project identity. The gateway can connect the inbound request to the outbound calls in one trace. LLM cost chargeback shows how token attribution at the egress point gives finance an exact split of the provider invoice.
Policy drift also slows incident response. A team that must block a model provider needs one change at the egress gateway. A team that must block a caller needs one change at the ingress gateway. One management plane keeps both changes in one audit log.
 Agent Router Enterprise
How Tetrate Agent Router Enterprise and Agent Router for Ingress Cover Both Directions
Agent Router Enterprise governs calls from your agents to model providers and MCP servers. The gateway applies model access rules, token limits, budgets, guardrails, and MCP egress control. The AI gateway performance benchmarks publish the data plane overhead and the test method.
Agent Router for Ingress governs requests coming into your agents and self-hosted models. The data plane runs in your cluster. Tetrate manages the gateway lifecycle, and your team sets routing and policy. Gateway API egress and GEP-4488 covers the standards work for outbound traffic. How to keep LLM API keys out of application code covers provider key handling at the egress gateway.
Tetrate built egress gateways in Tetrate Service Bridge for years before AI traffic arrived. Agent Router Enterprise applies the same egress pattern to models, tokens, and tools. Who created Envoy AI Gateway covers the open source project behind the data plane. Best enterprise AI gateway compares current enterprise AI gateways.
Availability and How to Get Started
Tetrate Agent Router Enterprise is available now for AI egress to model providers and MCP servers, with data planes you run in your cloud or on-premises network and a Tetrate-run management plane. Agent Router for Ingress covers inbound traffic to agents and self-hosted models in your cluster. Start with the Agent Router Enterprise docs for cost attribution, and book a demo to see both directions on your own traffic.
Frequently Asked Questions
What Is AI Ingress?
AI ingress is traffic coming into your agents and self-hosted models. An AI ingress gateway checks caller identity, token budgets, and rate limits before a request reaches your agent or your GPUs.
What Is AI Egress?
AI egress is traffic leaving your cluster for model providers and MCP servers. An AI egress gateway decides which destinations your agents can reach, adds provider keys on the way out, and counts tokens per team and agent.
Do Agents Create More Egress Traffic Than Ingress Traffic?
Yes, in most agent workloads. One user request can start many model calls and tool calls. Each model call and tool call leaves the cluster, so egress volume grows faster than ingress volume.
Can One Gateway Govern Both AI Ingress and AI Egress?
Yes. An Envoy-based data plane can receive inbound requests to agents and self-hosted models and can govern outbound calls to providers and MCP servers. One management plane keeps identity, policy, and audit in one place.
What Does an AI Egress Gateway Count?
An AI egress gateway counts tokens per team, agent, and project on each call. The gateway also records the model, the destination, and the caller key on each call for cost reports and audit.
Does Kubernetes Have a Built-In Egress Resource?
No. Core Kubernetes has no Egress resource. NetworkPolicy can limit outbound traffic by destination, and gateways and service meshes add outbound control points.
Sources
- Govern MCP server access, Tetrate docs
- Split the AI bill across the teams that caused it, Tetrate docs
- TSB egress gateway docs
- GEP-4488, Gateway API
Related: What is an AI gateway?, on the gateway layer between applications and model providers; F5 BIG-IP Next for Kubernetes vs. Tetrate Agent Router Enterprise, on AI ingress and egress compared with a network gateway.